
The Solution
HackNot Protects Your Data and Assures You a Peace of Mind
Overview
HackNot has developed a new architecture that uses two computing devices to secure sensitive information from malware affecting the user.
Typically, malware infiltrates a user’s environment from his computing device hereby referred to as the “legacy computing system”.
However, a second computing device will be used by HackNot to create a single, safe, and secure out-of-band communication channel, hereby referred to as the “secured site”.
HackNot’s architecture can secure all user input sessions including secured authentication, session integrity, and content validation.
Architecture Modification
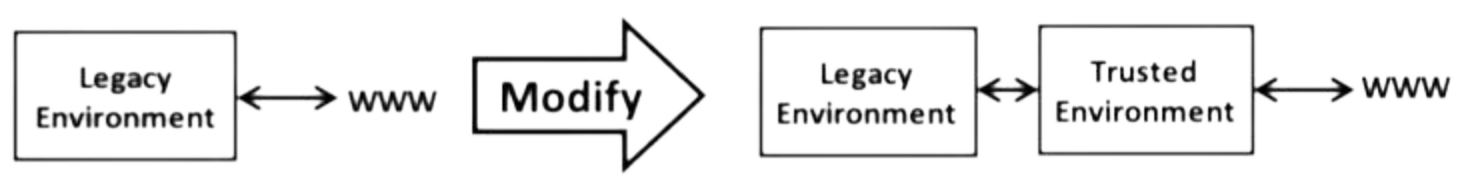
The diagram shows the architectural modification that will allow the protection of user critical data and applications.
Critical data, such as passwords, encryption codes, and email contact lists, are stored and maintained by the trusted environment.
Critical applications, such as encryption processes or firewalls, are shielded from the legacy environment.
This way, hackers installing malware in the legacy environment do not have access to the original and the encrypted document or may not tamper with the firewall URL lists to allow the hacker access to sites and computing systems without the user’s consent or the trusted environment control.
Providing Peace of Mind
HackNot’s architecture is focused on securing all user input sessions including secured authentication, session integrity, and content validation. In doing so, the user is protected even when a malware resides in his computer system:
- If the user downloads malware to his computer, the damage is minimized, contained, and reversible.
- “Contamination” of one computer system does not propagate to other computers.
- Infected computers are not posing risk to personal data, account numbers and passwords are protected, email distribution is avoided, undesired uploads to the WWW are stopped.
- The user identity is protected and irrefutable.
- A first attempt of malware to access the WWW is detected.
- Attempts to copy passwords (or other user’s information) will expose the hacker and his actions.